Legal News Update
Contributors: Almaida Askandar, S.H., MBA, Nita Damayanti, S.H., and Clarissa Felicia Hidriani, S.H.
Published on 4 October 2026 by IABF Law Firm, Jakarta, Indonesia.
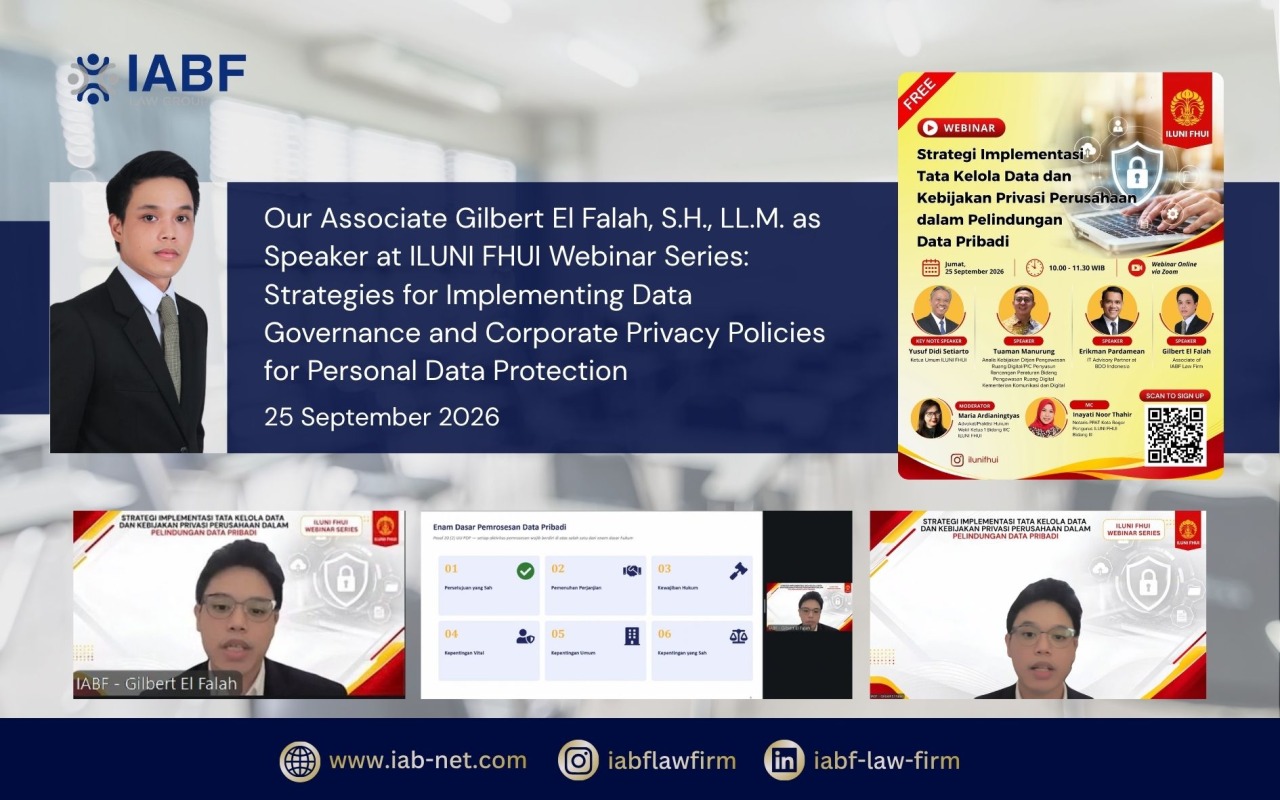
IABF Law Firm Participated in Webinar Series: Strategies for Implementing Data Governance and Corporate Privacy Policies in Personal Data Protection
Jakarta, 25 September 2026 — IABF Law Firm participated in webinar series held by The Alumni Association of the Faculty of Law, Universitas Indonesia entitled “Strategies for Implementing Data Governance and Corporate Privacy Policies in Personal Data Protection”, attended by participants from the corporate, financial services, and technology sectors. IABF Law Firm also participated in the event, with Mr. Gilbert El Falah, Associate at IABF Law Firm, serving as one of the three speakers. The webinar discussed the implementation of Law No. 27 of 2022 on Personal Data Protection (“PDP Law“) and its implementing regulations from three complementary perspectives, namely regulatory, cybersecurity, and compliance perspectives.
Summary of Discussion
Mr. Tuaman Manurung — Digital Space Supervision Policy Analyst, Ministry of Communication and Digital Affairs: Regulatory Landscape and Fundamental Compliance with the PDP Law
Opening the discussion from the regulatory perspective, Mr. Tuaman Manurung emphasized that the PDP Law has entered into force and its applicability does not depend on the issuance of implementing regulations. According to Mr. Tuaman, the obligations under the PDP Law are binding on all Personal Data Controllers and Personal Data Processors, including government institutions, private-sector entities, and international organizations, insofar as they process data relating to Personal Data Subjects who are Indonesian citizens.
He highlighted a common misconception whereby organizations immediately formulate compliance plans without first understanding the meaning and classification of Personal Data, which is divided into general Personal Data and specific Personal Data, the latter of which requires more restricted handling. Mr. Tuaman also underlined the importance of clearly allocating the roles of each party in a written agreement, while emphasizing that a Personal Data Controller cannot contractually relinquish its accountability towards Personal Data Subjects, although it may retain its right of recourse against a Personal Data Processor.
Another recurring misconception, according to him, is the assumption that consent constitutes the sole or primary lawful basis for processing. In fact, there are six lawful bases for processing, including the performance of contractual obligations, compliance with legal obligations, and the performance of duties and activities in the public interest. He referred to the installation of CCTV as an example, where a notice should be displayed before an individual is recorded by the camera, thereby allowing the individual to make an informed decision as to whether to enter the relevant area.
Mr. Tuaman concluded his session by emphasizing one fundamental principle: organizations should shift away from the paradigm of treating Personal Data as a corporate asset and instead begin viewing it as information entrusted to them by Personal Data Subjects.
Mr. Erikman Pardamean — IT Advisory Partner, BDO Indonesia: Technology and Cybersecurity in Personal Data Protection and Organizational Readiness
Mr. Erikman Pardamean addressed the topic from a technical and cybersecurity perspective. He observed that Personal Data within modern organizations is rarely stored in a single location. Instead, such data is distributed across websites, applications, application programming interfaces connecting various systems, databases, cloud platforms and software-as-a-service solutions, CCTV and IoT devices, analytics tools and artificial intelligence applications, as well as third-party vendor environments. According to him, a failure at any one of these points may disrupt business operations and adversely affect a company’s reputation.
From an implementation perspective, Mr. Erikman recommended a structured sequence beginning with data inventory and data flow mapping, accompanied by formal assessments including a Record of Processing Activities (“ROPA“) and a Data Protection Impact Assessment (“DPIA“). He emphasized that privacy controls should be embedded from the earliest stages of the system development lifecycle, starting from planning and design and continuing through development, testing, and implementation.
He further recommended that organizations begin with the most critical, practicable, and mandatory fundamental controls, such as data inventories, access controls, encryption, Personal Data incident and breach tracking, and evidence retention, and subsequently develop these controls through monitoring and continuous improvement.
Mr. Gilbert El Falah — Associate, IABF Law Firm: Privacy Operation Lifecycle, Mandatory Documentation, and Comparison with the GDPR
Mr. Gilbert El Falah structured his presentation around four principal themes: the privacy operation lifecycle, the suite of PDP documentation, governance, and a comparison between the Indonesian regime and the General Data Protection Regulation (“GDPR”).
In explaining the privacy operation lifecycle, Mr. Gilbert stated that, from the outset, a Personal Data Controller should determine what data will be collected, establish the lawful basis for processing before the collection takes place, and provide the required information to Personal Data Subjects.
With respect to consent, he highlighted two circumstances that require particular attention. First, combining several purposes into a single consent request, for example, one consent simultaneously covering marketing purposes and other unrelated purposes. Second, combining consent with acceptance of terms of use, as commonly seen in a single checkbox stating, “I agree with the terms of use and the privacy policy,” which effectively eliminates a genuine choice for the Personal Data Subject. According to him, the information accompanying a consent request should include the lawful basis for processing, the purpose of processing, the type of data and its relevance to such purpose, the retention and processing periods, and the rights of the Personal Data Subject.
Mr. Gilbert then elaborated on the categories of documentation that an organization should maintain, namely: (i) policies and notices; (ii) consent and assessments; (iii) agreements with third parties; and (iv) governance documentation.
Within the first category, he distinguished between a privacy policy, which is a general overarching document governing processing activities throughout an organization, and a privacy notice, which is specific and provided to Personal Data Subjects when their data is collected, for example, through a website.
Within the second category, organizations should prepare documents such as consent forms, Legitimate Interest Assessments (“LIA“), and DPIAs.
With respect to agreements with third parties, he explained that organizations generally need to prepare Data Processing Agreements, Joint Controller Agreements, NDAs, and mechanisms for data transfers. He further explained that cross-border transfers of Personal Data require the relevant overseas data transfer mechanism to first be established, namely through an adequacy list, safeguards, and consent, which operate on a hierarchical basis. He also described the types of safeguards that may be used by Personal Data Controllers, including standard contractual clauses and binding corporate rules, with the latter generally being used for internal data transfers within multinational corporate groups.
As for the final category, namely governance documentation, organizations should maintain a ROPA and a letter appointing a Data Protection Officer (“DPO“). Mr. Gilbert concluded his presentation by highlighting several comparisons between the GDPR and the PDP Law.
Question and Answer
Question 1 (Ms. Heni): To what extent is a company, acting as a Personal Data Controller, responsible where a data breach or misuse occurs at a vendor or third party that receives the data for processing?
Mr. Gilbert El Falah explained that the answer depends on the legal capacity in which the relevant party acts, namely whether it acts as a Personal Data Processor, Joint Personal Data Controller, or Sub-Processor.
Where the party acts as a Personal Data Processor, responsibility remains with the Personal Data Controller. Where the party acts as a Joint Personal Data Controller, responsibility is shared among the relevant Personal Data Controllers. Meanwhile, a vendor acting as a Personal Data Processor becomes responsible where it processes Personal Data outside the instructions of the Personal Data Controller.
Mr. Gilbert specifically highlighted circumstances in which a Personal Data Processor processes Personal Data without instructions from the Personal Data Controller. In such circumstances, the Personal Data Processor is treated as a Personal Data Controller in respect of that processing and assumes the corresponding responsibilities, as it processes the data on its own initiative.
Mr. Erikman Pardamean added that the cause of an incident should be identified in order to determine its practical implications, and emphasized the importance of having appropriate systems, tools, or monitoring mechanisms available to address incidents when they occur. He noted that although processing activities may be outsourced, accountability does not automatically transfer to the vendor and instead remains with the Personal Data Controller. Even where an organization uses a cloud provider or other vendor, the organization remains the Personal Data Controller and therefore remains accountable for the protection of the data, while the vendor does not assume such accountability.
Question 2 (Mr. Pratomo): Who holds ultimate accountability for Personal Data protection at the corporate level, and how should responsibilities be allocated among the Board and Management, Legal, the Data Protection Officer or privacy function, IT Security, and business units?
Mr. Erikman Pardamean explained that ultimate responsibility rests with the Board and Management as the bodies responsible for directing the organization, while day-to-day implementation takes place at different levels. He described this through the three-lines model.
Business process owners or business departments bear first-line responsibility for execution. The second line — comprising Legal, the privacy function and Data Protection Officer, together with IT Security and human resources — provides support and oversight. The third line, namely internal audit or the assurance function, provides independent assurance and independent testing to ensure that the privacy framework is properly implemented.
Mr. Tuaman Manurung supplemented this explanation from a normative perspective, emphasizing that accountability remains with the Personal Data Controller. A Personal Data Controller may appoint a Personal Data Processor, but such appointment does not transfer accountability. This is precisely why legal instruments are important. A Data Processing Agreement, where a Personal Data Controller appoints a Personal Data Processor, or a Joint Controller Agreement, where the relationship is between Personal Data Controllers, reinforces the principle that accountability is not transferred.
According to Mr. Tuaman, the subject recognized under the PDP Law is not the “company” in the conventional sense, but rather the Personal Data Controller. Accordingly, the relevant entity must be identified. A Personal Data Controller may be an individual, legal entity, or international organization, and the question of who controls the data should be answered by reference to the relevant entity.
He also noted a distinction from the GDPR, which recognizes the concepts of a third party and recipient, whereas the Indonesian framework only recognizes the Personal Data Controller. Consequently, insofar as a party processes Personal Data, it must be accountable, transparent, and responsible, and must be capable of demonstrating evidence of its compliance. Accordingly, the allocation of internal functions is primarily a matter of corporate governance and detailed internal delegation.
Closing Statement
The three speakers concluded the webinar with their respective messages. Mr. Tuaman Manurung encouraged organizations not to wait for the establishment of the PDP Institution and the issuance of implementing regulations before taking action.
Mr. Erikman Pardamean emphasized the PDP Law as the primary reference and overarching framework, while international standards such as ISO may be adopted as supporting tools.
Mr. Gilbert El Falah closed with a similar message, recommending that organizations begin with small steps, starting with data mapping to understand what data they hold, followed by identifying the associated risks and benchmarking against relevant metrics.
***
Disclaimer
This news update is prepared for general informational purposes only. The content does not constitute legal advice, a legal opinion, or counsel from IABF Law Firm. The information contained herein may not reflect the most current developments. Any quotation, distribution, or use of this information for any purpose is solely at the user’s own risk.